When hackers turn off the fridges: cyberattacks can destroy more than data
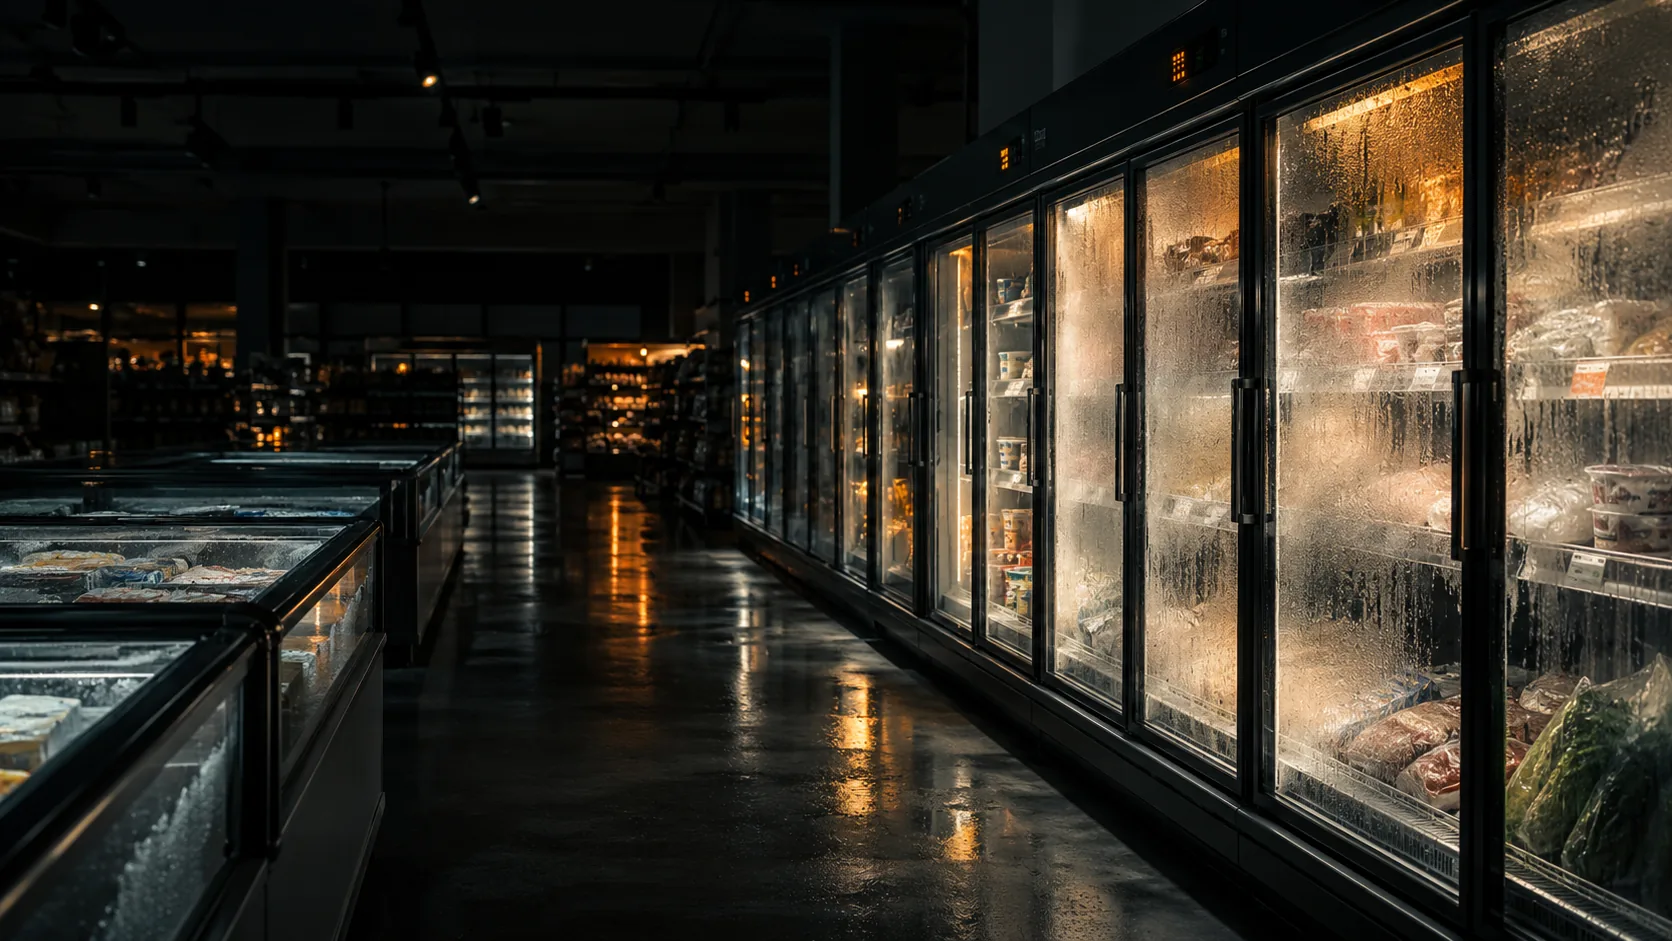
When most managers hear “cyberattack”, they think of stolen files, locked computers or a demand for ransom. In France this week, the impact was far more tangible: refrigerators began heating up.
During the night of 11 to 12 October 2026, attackers remotely interfered with the refrigeration systems used by hundreds of supermarkets. Stores had to remove and destroy chilled and frozen products. Some equipment reportedly reached temperatures of up to 50°C, and isolated fires were also reported.
The incident is a useful warning for every business with connected machinery, building controls or operational equipment. A cyberattack does not need to steal a single customer record to cause serious financial loss. It can change how physical equipment behaves.
A cyberattack with physical consequences
Intermarché said that roughly 150 to 200 of its stores were affected, while Coopérative U reported almost 100. Carrefour and Monoprix also confirmed disruption at a smaller number of locations. The Paris public prosecutor opened an investigation and France's national cybersecurity agency, ANSSI, is investigating the incident.
The affected systems controlled commercial refrigeration equipment. Instead of keeping products cold, compromised controllers reportedly initiated or prolonged defrosting cycles. A normal maintenance function became a way to damage stock and interrupt store operations.
The consequences were immediate:
- chilled and frozen food could no longer be sold safely;
- employees had to empty cabinets and isolate affected products;
- stores lost stock and sales while equipment was checked;
- technicians and incident-response teams had to intervene urgently; and
- the failure created potential safety risks as well as financial ones.
At the time of writing, the technical investigation is continuing. Public reporting indicates that affected equipment was running outdated firmware, but the precise entry point and vulnerabilities used have not been formally established. That distinction matters: companies should act on the lessons without treating early reports as a completed forensic conclusion.
Why connected refrigeration is cyber-physical infrastructure
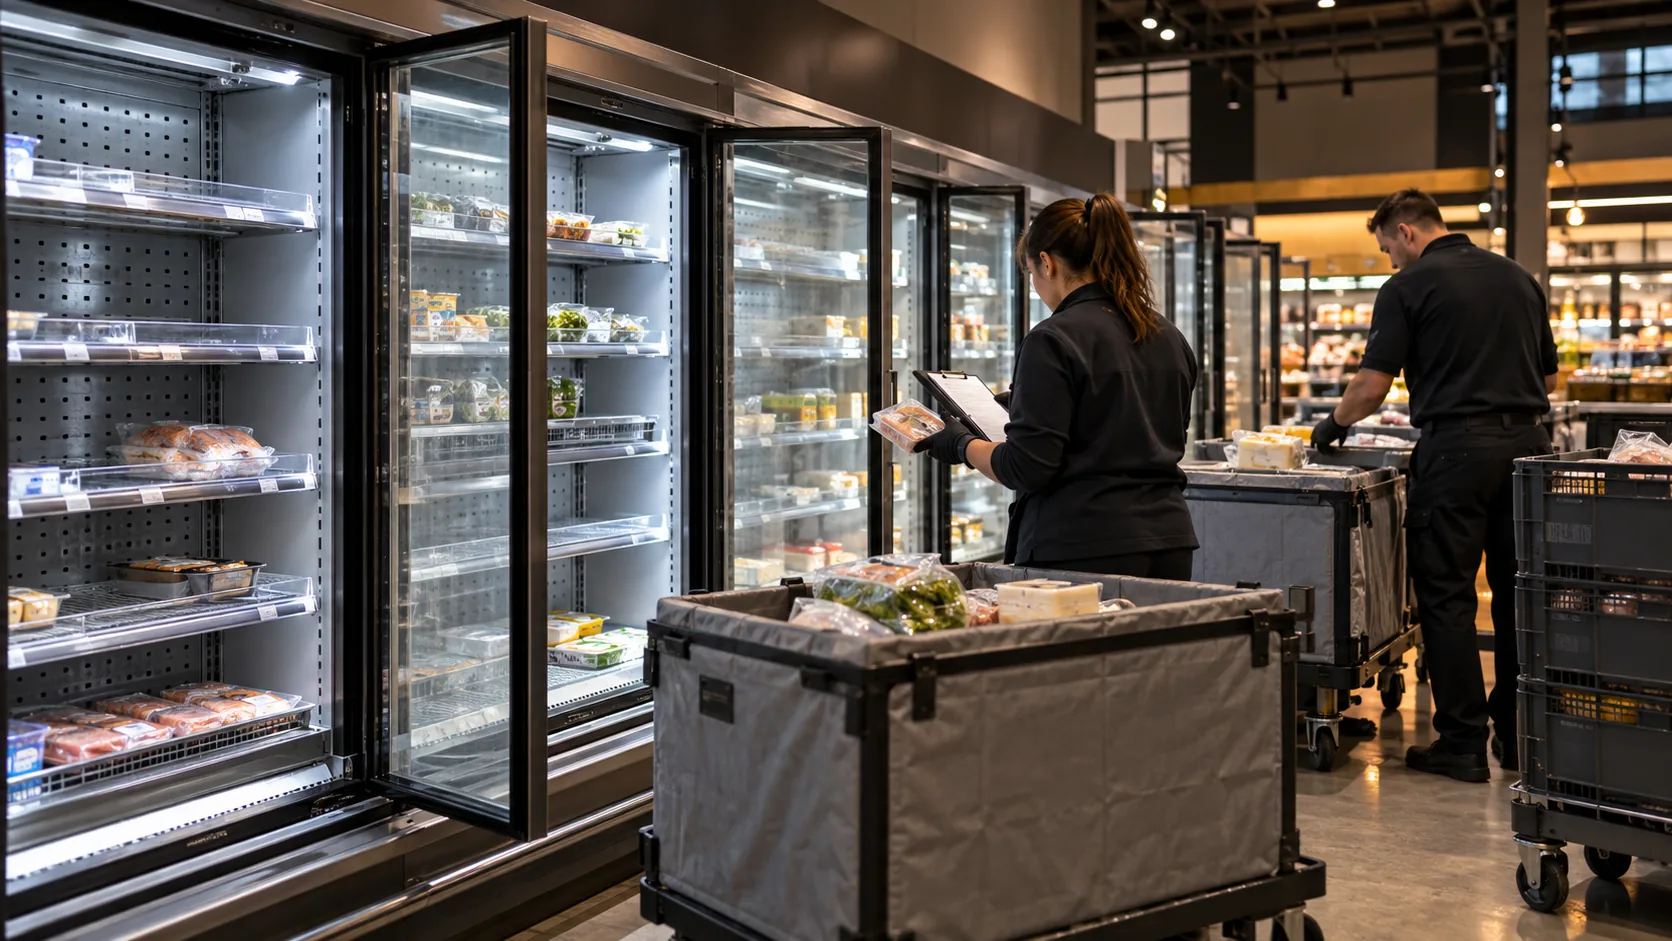
Modern commercial refrigeration is not a collection of independent refrigerators. A central controller may manage temperatures, alarms, compressors, defrost cycles and energy use across an entire site. Remote access allows a maintenance company or equipment supplier to diagnose faults without travelling to every store.
This connectivity is useful. It also means that one poorly protected management interface can influence many physical devices.
Security researchers had previously identified vulnerabilities in some Danfoss refrigeration controllers, including weaknesses that could allow unauthorised control or disruption. Danfoss addressed those issues in firmware version 4.3.1 and advises customers to use current firmware and avoid exposing management interfaces directly to the internet. This does not prove that those specific vulnerabilities caused the French incident; it shows why patching and exposure management matter for operational equipment, not only laptops and servers.
Cybersecurity is no longer only about data
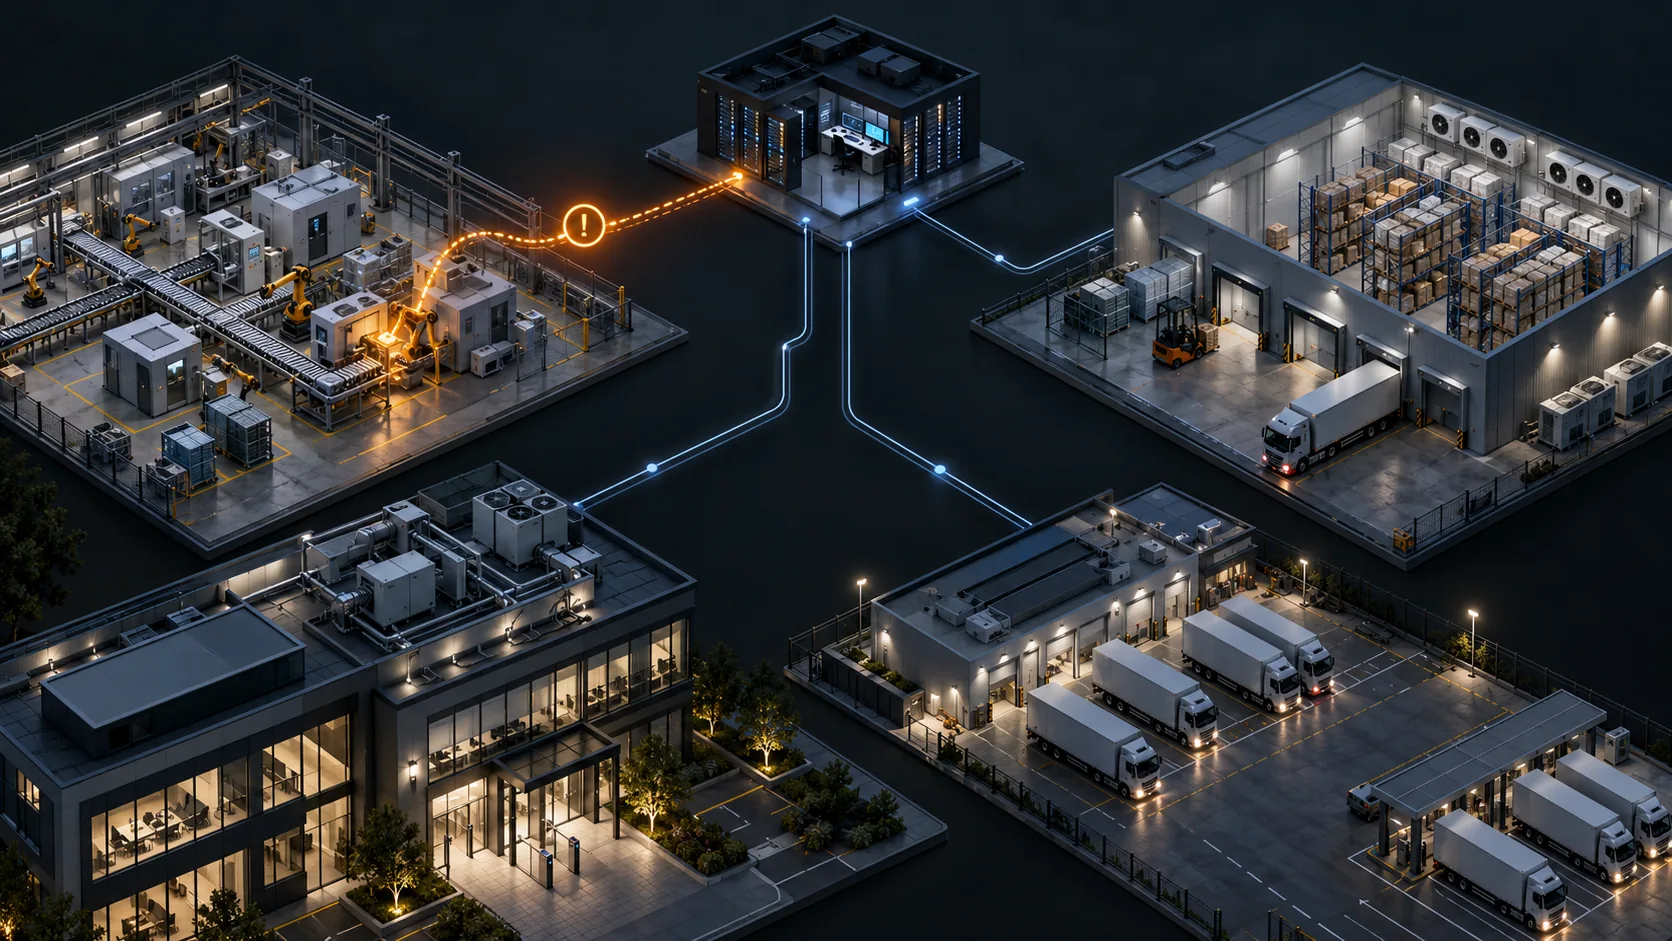
The boundary between information technology and physical operations has largely disappeared. The same pattern can affect many sectors:
- Factories: connected production lines, robots and industrial controllers can be stopped or given unsafe instructions.
- Warehouses: temperature, humidity, doors and automated handling systems can affect entire inventories.
- Commercial buildings: heating, ventilation, lifts, cameras and access-control systems increasingly depend on networks and remote management.
- Logistics: fleet tracking, route planning, fuel management and depot systems can interrupt deliveries.
- Hotels: room access, reservations, payment systems and building controls are closely connected to daily operations.
- Retailers: point-of-sale systems, digital pricing, refrigeration and inventory management all influence whether stores can trade.
In each case, the cyber risk is also an operational, financial and sometimes safety risk. The security programme therefore cannot end at email, antivirus and Microsoft
- It must include the systems that keep the business running.
What this means for companies operating in China
Many companies in China have invested in endpoint protection, firewalls and cloud security. Their operational systems may have received less attention, particularly when machinery was installed by a supplier and is maintained remotely.
Common blind spots include:
- equipment that no longer receives firmware updates;
- internet-facing administration pages installed for convenience;
- shared supplier accounts with weak or unchanged passwords;
- remote support tools that do not require multi-factor authentication;
- factory and office networks that are insufficiently separated;
- maintenance connections that remain active when no work is being performed; and
- alarms that depend on the same controller being attacked.
These conditions are not limited to large industrial groups. A restaurant chain, hotel, laboratory, warehouse, retailer or property manager may depend on connected equipment without describing it as “operational technology”. The name is less important than the consequence: if changing a digital instruction can stop operations or damage a physical asset, it belongs in the cybersecurity scope.
Five questions management should ask
You do not need to understand refrigeration protocols or industrial control code to govern this risk. Start with five practical questions:
- What connected equipment could stop operations, damage stock or create a safety issue if it behaved incorrectly? Include machinery, sensors, building systems and vendor-installed controllers.
- Which of those systems can be reached remotely, and by whom? Identify public internet exposure, VPN access, supplier tools, shared accounts and unattended maintenance connections.
- Who is responsible for updates and security fixes? Confirm firmware versions, support status, maintenance contracts and a realistic patching process.
- Would we detect abnormal physical behaviour independently? A temperature alarm controlled by the same compromised device may not provide reliable warning.
- Can the business operate and recover without the connected system? Define safe shutdown, manual procedures, product-isolation rules, escalation contacts and restoration priorities.
If the answers are unclear, management has already found the first problem: nobody has an accurate view of the operational dependency.
Practical controls that reduce the risk
The objective is not to disconnect every useful system. It is to make remote control deliberate, limited and observable.
Build an inventory around business impact
Record critical connected equipment, its owner, its location, its firmware or software version, how it communicates and what would happen if it failed. Prioritise systems by operational consequence rather than by purchase price.
Restrict remote access
Do not publish management interfaces directly on the internet. Use controlled VPN or secure access services, individual accounts, multi-factor authentication and least privilege. Activate supplier access only when needed where practicable, and retain logs of the connection.
Separate operational and office networks
Segmentation limits how far an attacker can move after compromising a laptop, supplier account or exposed device. Access between zones should be explicitly required, not available by default.
Maintain firmware and vendor support
Include operational equipment in vulnerability and patch management. When an update cannot be installed immediately, document the reason, add compensating controls and set a decision date. Unsupported equipment is a business risk that management should see and accept—or replace.
Monitor the physical process
Use independent alarms and sensible operating thresholds for critical conditions such as temperature, pressure, access or equipment state. Monitor administrative logins and configuration changes as well as network availability.
Prepare a physical response
An incident plan should say more than “call IT”. It should identify who can isolate equipment, protect people and stock, contact the maintenance provider, move to manual operations and decide when a site can safely reopen. Test those decisions before a real incident compresses the timeline.
The management takeaway
The French supermarket attack makes an abstract risk visible. Connected equipment can improve efficiency and reduce maintenance costs, but it also gives digital instructions a physical consequence.
The first management action is simple: identify the connected systems whose failure could stop the business, damage assets or affect safety, then verify who can reach them remotely. That one exercise usually reveals where technical hardening, supplier governance and continuity planning should begin.
APIS Consulting helps companies in China assess connected operational systems, harden remote access, review supplier controls and train both technical and management teams. Contact us to discuss a focused review, or start with our free cybersecurity audit.
Sources
- AFP: French supermarket chains say cyberattack forced refrigerator shutdown
- ABC News: French supermarkets hacked, causing fires and food loss
- Claroty Team82: vulnerabilities in Danfoss refrigeration controllers
- Danfoss security advisory DSA-2025-08-01
- Danfoss AK-SM 800A firmware and software downloads
This article reflects public information available on 13 October 2026. The incident investigation is continuing, and technical findings may change.